


Blog
AI Agents Are Already Accessing Bank Accounts. Can Banks Detect Them Before It’s Too Late?
As AI agents begin operating inside customer bank accounts, typing biometrics could provide a missing layer of fraud protection. The next fraudulent bank transaction might come from an AI agent using perfectly valid credentials. Would the bank notice before the money moves? This is no longer a distant hypothetical. In October 2026, Axios reported that…
What If Your Next 10,000 Logins Weren’t Human?
Imagine a swarm of AI agents logging into your platform tomorrow, using your real customers’ stolen credentials. Would your security team even notice? AI agents are becoming increasingly capable of navigating websites, interacting with applications, and performing complex tasks autonomously. That’s great when they’re programmed by you. But what happens when attackers use them to…
The Best Alternative to Hardware Security Keys – It’s Not What You Think
If you’re looking for an alternative to hardware security keys like YubiKey, you will find plenty of options: passkeys, authenticator apps, Windows Hello, smart cards, other hardware tokens. But most of these alternatives have something in common. They replace one authentication device with another. There is another option: don’t use an additional device at all….
Introducing TypingDNA Human Likeness – A Novel Bot Detection for the AI Age
For years, customers and partners have asked us whether typing biometrics could help distinguish natural human typing from synthetic or automated input. That question is becoming more important as bots, browser automation, scripted form filling, and AI agents become increasingly capable of interacting with websites and applications in ways that may appear human. We decided…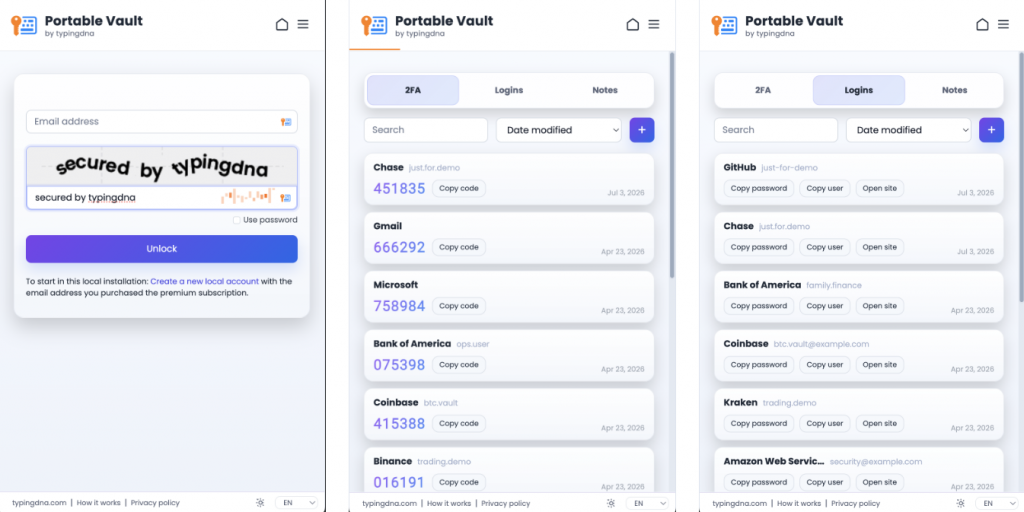
Finally, a Portable Vault for 2FA, Passwords, and Secure Notes, Secured by TypingDNA
Built for organizations who want a portable phone-free 2FA authenticator and vault for sensitive information, running on Mac, Windows, and Linux. For a long time, there has been a gap between simple authenticator apps and full password managers. One gives you 2FA codes but little else. The other often pushes you toward a cloud vault,…
The Corporate 2FA Blind Spot: What Happens When Phones Are Banned?
Most corporate MFA policies were designed with one assumption baked in: employees have a smartphone. For a significant portion of the workforce, that assumption is wrong – not because of personal preference, but because of company policy. 1. The Industries Where Phones Are Already Banned This is not a hypothetical. Across several major verticals, personal…
Using Windows Hello as 2FA for Microsoft Entra? Here’s the Uncomfortable Truth
This article focuses on Windows Hello for Business as used within Microsoft Entra ID (formerly Azure AD) MFA flows. Many of the same principles apply to other desktop-based authentication methods like Okta Fastpass. 1. Windows Hello Is Not 2FA Windows Hello lets users unlock their Windows device using either a biometric (fingerprint or face recognition)…
YubiKey or Nothing? There’s a Third Option.
Hardware security keys are the gold standard of enterprise 2FA. No serious security professional disputes that. The problem is not the YubiKey’s security properties – it is everything that comes with running them at scale. 1. The Real Cost of Hardware Keys at Scale The operational model for hardware security keys breaks down quickly in…